
MendasDigital
Level 1
Write the reason you're deleting this FAQ
#!/bin/bash
length='10000'
head -c "$length" /dev/urandom | base64 -w 0 | sed 's/=//g' | sed 's///#/g' | sed 's/+/$/g' | head -c "$length" > password
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
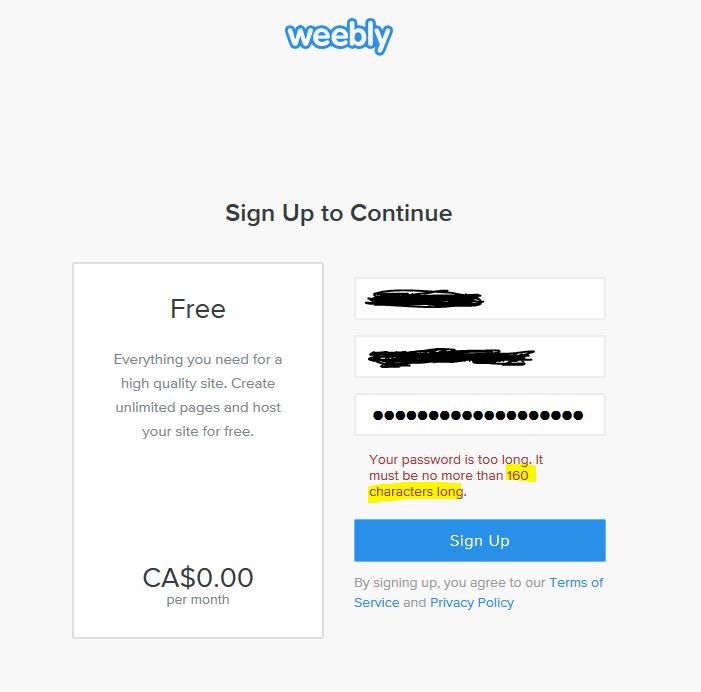
 I think 160 characters is good for the time being, but I reckon once hackers improve their scripts we will have passwords that will even reach 1000 characters. Password apps will be mandatory when that will inevitably happen. I think I'll just invest in some stocks for KeePass now that I think about it. :D
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
Are you sure you want to delete this post?
ninjasalesgroup
Are you sure you want to delete this post?